
Partner Article
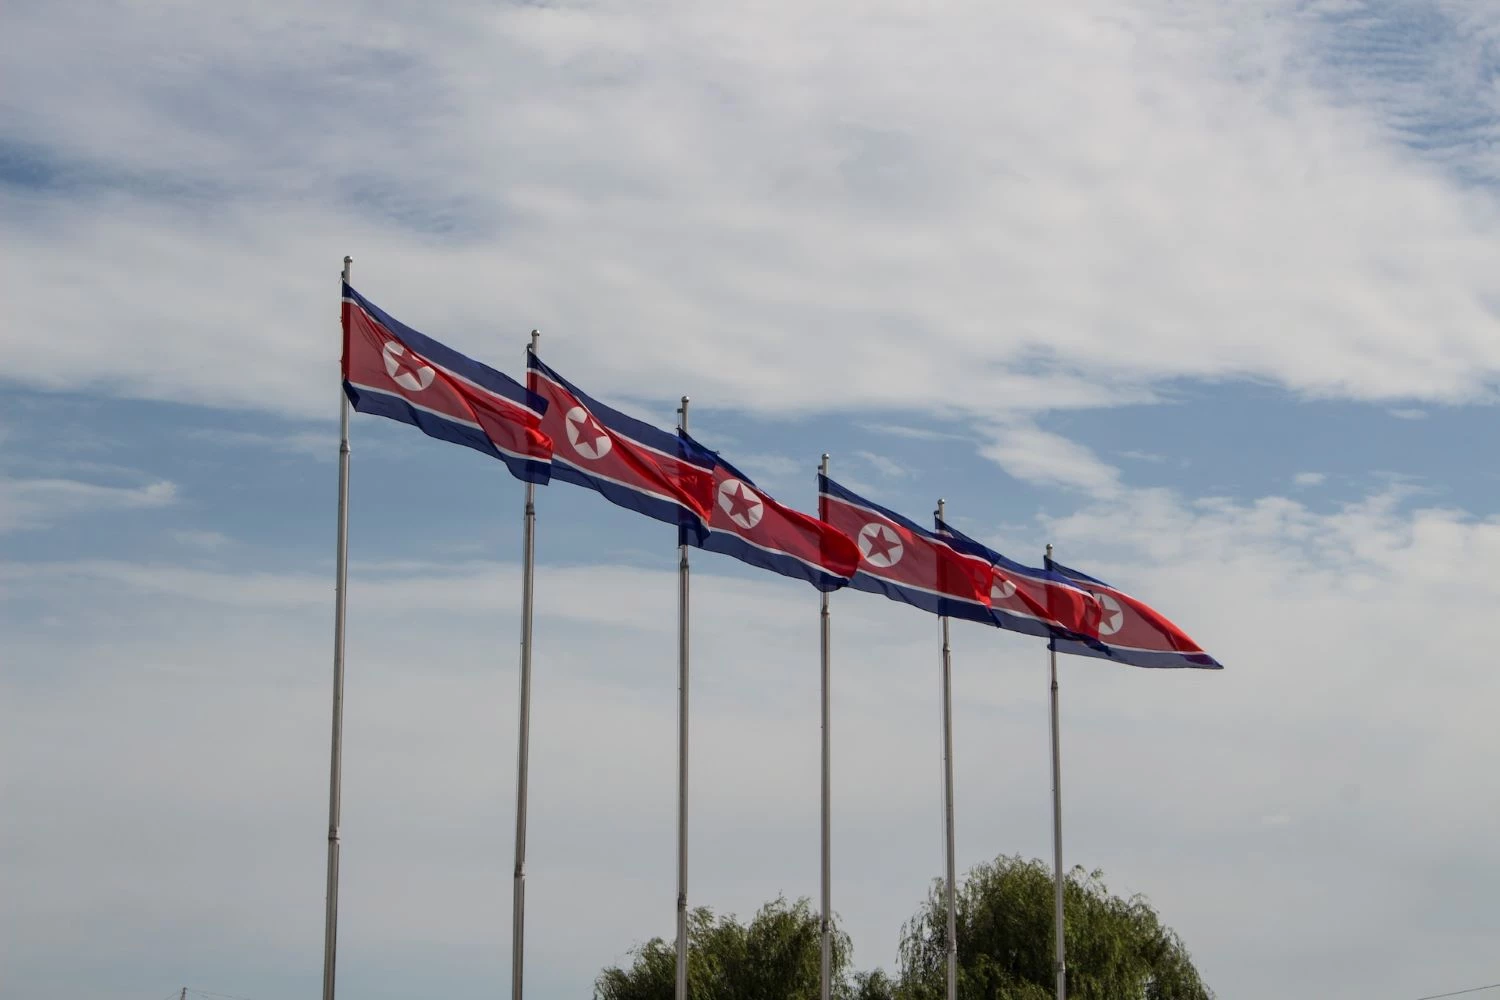
North Korean APT implicated in JumpCloud hack
In recent news, the cloud-based IT management service JumpCloud publicly shared details gathered from the investigation into an intrusion on their network. Having reviewed the newly released indicators of compromise, SentinelLabs associated the cluster of threat activity to a North Korean state sponsored APT.
The indicators of compromise (IOCs) are linked to a wide variety of activity SentinelLabs attributed to the Democratic People’s Republic of Korea (DPRK), overall centric to the supply chain targeting approach seen in previous campaigns.
Additionally, based on the IOCs shared by JumpCloud, SentinelLabs were able to analyse the threat actor’s infrastructure and, by mapping it out, they showed the links between the diverse set of IP addresses and pick up various patterns.
SentinelLabs have shared their analysis in a report published today.
Conclusion
It is evident that North Korean threat actors are continuously adapting and exploring novel methods to infiltrate targeted networks. The JumpCloud intrusion serves as a clear illustration of their inclination towards supply chain targeting, which yields a multitude of potential subsequent intrusions. The DPRK demonstrates a profound understanding of the benefits derived from meticulously selecting high-value targets as a pivot point to conduct supply chain attacks into fruitful networks.
This was posted in Bdaily's Members' News section by P Adams .
Our Partners
 Are you a meat proxy?
 Engaging the five-generation workplace
 Talent is an asset, not an operational resource
 Taking advantage of the opportunities ahead
 Accountability isn’t the enemy of empathy
 Act now to avoid a last-minute tax scramble
 How inner-city living can transform a city by the sea
 Artificial intelligence's value is the time it gives back
 Why we must break the magnetic pull of London
 AI scepticism is healthy - inaction isn't
 What does NPPF mean for planning gain and pricing?
 What new NPPF rules mean for landowners